Last Updated on 13.10.2026 by Danylo T
Electronic signatures have quietly become the default way businesses agree to things. Your contracts, offers, NDAs and invoices now move through email instead of printers. So the question is no longer whether you can sign a document electronically. It is whether that signature holds up later, when someone disputes it.
In this article, you will find the practices that keep electronic signatures legally binding, secure and compliant, the rules that decide whether a signature counts at all, and the checks worth running before you send an important document out for signing.
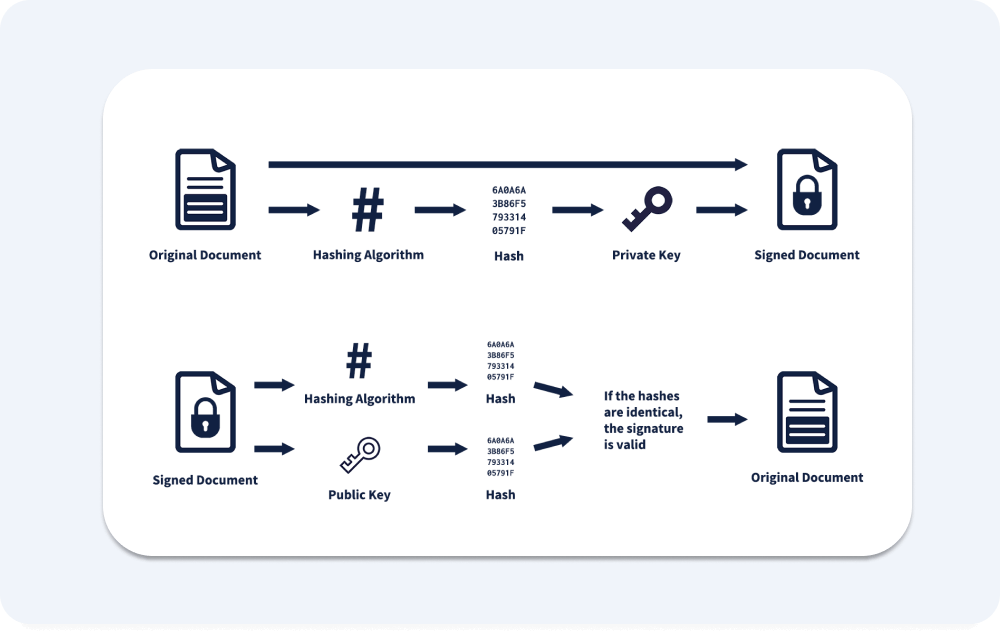
source: Techterms
Of course, to make the most out of digital signatures, you need to know the best practices. So let’s talk about the best ways to implement digital signatures to lock down those crucial company documents. Sounds good?
Key Takeaways
Six things do most of the work in keeping your electronic signature defensible:
👉 Choose a platform that supports ESIGN, UETA and eIDAS compliance out of the box.
👉 Verify the signer’s identity at a level that matches the document’s risk.
👉 Capture clear consent to sign electronically, and clear intent to be bound.
👉 Keep a complete audit trail with timestamps, and store it with the document.
👉 Protect document integrity so any change made after signing is detectable.
👉 Know which documents still need a wet-ink or qualified signature.
What Is an Electronic Signature?
An electronic signature is any electronic sound, symbol or process attached to a document that shows a person agreed to it. That definition sounds broad because it is meant to be. The law generally cares about what your signature proves, not about what it looks like, so it does not have to resemble handwriting for you to rely on it.
In practice, the electronic signing methods you will meet come down to a few forms:
- A name typed into a signature field
- A click on an “I agree” or “Sign here” button
- A scanned image of a handwritten signature
- A certificate-based digital signature backed by a digital certificate
That last one is where most of the confusion starts, because a digital signature is a specific kind of electronic signature rather than a synonym for it. So before you decide how much verification your documents need, it helps to see the two side by side.
Electronic Signature vs. Digital Signature: What’s the Difference?
Every digital signature is an electronic signature, but the reverse is not true. A digital signature uses public key infrastructure to bind the signer’s digital certificate to the document, so any later change to the file breaks the seal. A plain electronic signature may carry no cryptography at all, which is why two signatures that look identical on your screen can be worth very different things in a dispute.
| Type | What it means | Security level | When to use it |
|---|---|---|---|
| Electronic signature | Any electronic mark showing intent to sign | Basic, depends on the platform | Internal approvals, low-risk agreements |
| Digital signature | Certificate and PKI based, tamper-evident | High, cryptographically verifiable | Contracts, finance, anything disputable |
| Qualified or secure electronic signature | A digital signature issued on a qualified certificate after identity checks | Highest, strongest legal status | Regulated industries, cross-border deals, public registries |
So the right choice depends on what your document has to survive. A holiday request needs far less than a supplier contract you may have to defend in front of a regulator, and matching the two is the first of the security and compliance decisions you will make.
What Makes an Electronic Signature Legally Valid?
In most jurisdictions your electronic signature is legally valid when four things can be shown: the signer agreed to do business electronically, meant to sign, can be reliably identified, and the signature is reliably tied to the document that was signed. Courts and regulators look at that evidence rather than at the signature graphic itself, so this is what you are really collecting every time you send a document out.
1. Consent to transact electronically. The signer has to accept that the agreement will be signed and delivered electronically, and your platform should record that acceptance rather than assume it.
2. Intent to sign. A signature only counts if the person meant it as one, so your signing step needs a deliberate action and not a pre-ticked box.
3. Reliable identification of the signer. You need reasonable proof that whoever signed is who they claimed to be, but how much proof is reasonable depends on the document.
4. Reliable association with the document. The signature, your audit trail and the final signed version have to stay attached, so nobody can argue that a different document was signed.
Miss one of the four and the signature still exists, but its legal validity becomes something you have to argue rather than something you can show.
Key Electronic Signature Laws and Compliance Standards
You have already met eIDAS and the ESIGN Act above, in the list of standards your platform should align with. They are worth a closer look, because they are what turns “we both clicked” into an agreement you can enforce, and because the rules shift depending on where your signer sits.
United States: ESIGN Act and UETA. The federal ESIGN Act and the Uniform Electronic Transactions Act, adopted in most states, both say a signature cannot be denied legal status simply for being electronic. Between them they set the consent and intent requirements that most US electronic transactions rely on, so if you sign with American counterparties, this pair is your baseline.
European Union: eIDAS. eIDAS sorts electronic signatures into three tiers. A simple one is the basic case, an advanced electronic signature adds verified signer identity and tamper detection, and a qualified signature is an advanced one issued on a qualified certificate. Only that top tier carries the same weight as a handwritten signature across every member state, which is why you will see it demanded in property, corporate and public registry filings.
Canada: PIPEDA. PIPEDA recognises electronic documents and signatures at the federal level, while individual provinces run their own equivalent acts. So for anything with a Canadian counterparty it is worth checking which of the two applies to you.
Data protection: GDPR and its equivalents. Signing generates personal data, so where you store signed files, IP addresses and identity evidence falls under data protection rules as much as under signature law. Your retention limits apply to the audit trail too.
This is general information about electronic signature compliance, not legal advice. For high-value or cross-border agreements, check the requirements with a qualified lawyer in the relevant jurisdiction.
1. Choose a Compliant Electronic Signature Platform
When it comes to digital signature software, it’s not just about picking the most user-friendly option, but also ensuring it’s secure and legally compliant. Here’s why this is crucial:
Seamless Workflow Integration
The best digital signature software integrates seamlessly into your existing workflow. This means its integration capabilities should cover the other tools you use, like document management systems or CRM platforms. The easier it is to integrate, the smoother your processes will be.
Adaptability To Different Use Cases
A good software adapts to various scenarios – whether you’re signing a legal contract, a sales agreement, or an internal document (invoices, purchase orders, contracts etc.). The flexibility to handle different types of documents and use cases is a big plus.
Compliance With International Standards
Software that aligns with standards like the eIDAS in the EU or the ESIGN Act in the US gives you a safety net. These regulations are like a seal of approval that the software meets high security and legal standards.
Industry Recognition
If a software is well-regarded in the industry, it’s a good sign. It means that many have tested its robustness and trust it.
Using trusted software like this free pdf editor or others you prefer can ensure that your signatures hold up legally and are less likely to be compromised.
2. Protect Private Keys, Certificates and Signing Credentials
Your private key is like the secret ingredient to your signature’s security recipe. Here’s how to keep it under lock and key:
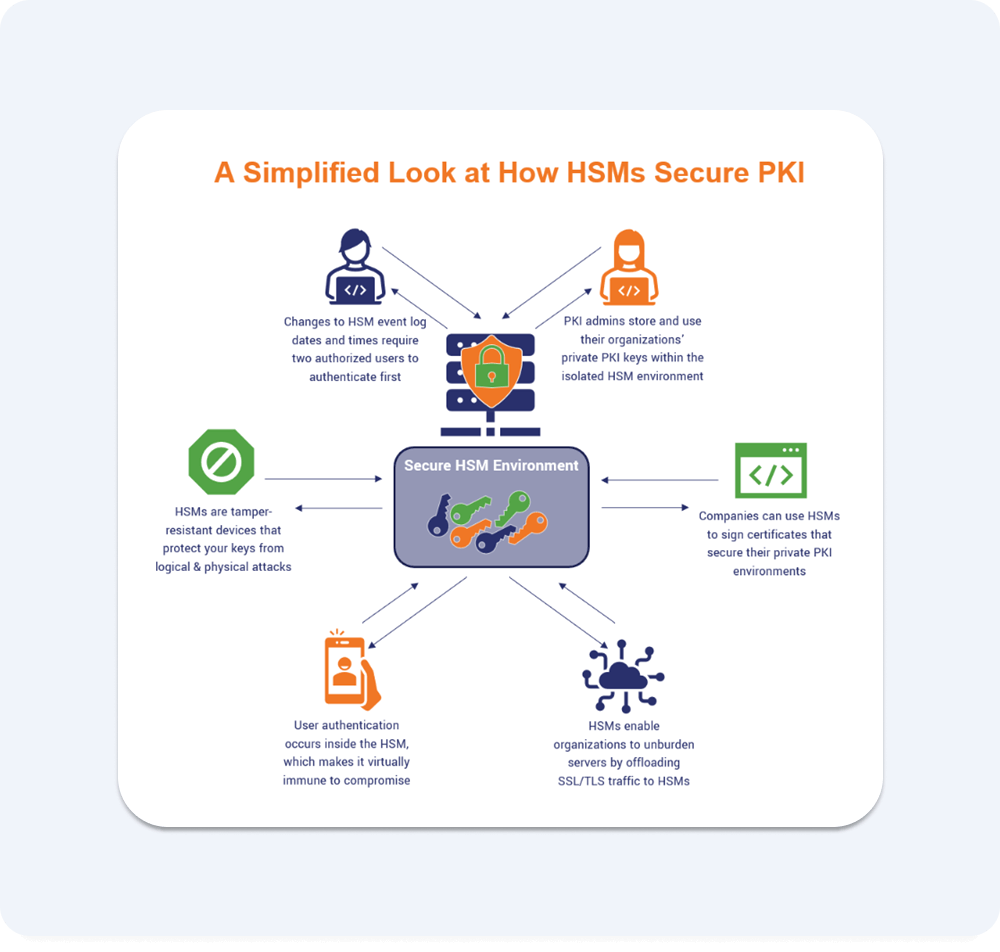
Hardware Security Modules (HSMs)
These are physical devices that safeguard and manage digital keys. They’re like a digital vault for digital business cards, making it extremely difficult for unauthorized users to access your private key.
source: Thesslstore
Trusted Platform Modules (TPMs)
These are integrated into your computer and provide a similar level of security for your keys.
Regular Key Updates
Updating your private keys at regular intervals is a smart move. This practice reduces the risk of your key being compromised over time.
Strong Access Controls
Only those who absolutely need to use the key should have access, and their access should be monitored and controlled. It’s all about ensuring that only the right people, under the right conditions, get to use or even see your private key.
It’s important to note that while private keys are essential for creating digital signatures, they only guarantee the authenticity of the signed data. To ensure secure transmission of the signed data between the sender and receiver, SSL/TLS certificates are also necessary. These certificates encrypt the communication channel, protecting it from eavesdropping and tampering.
3. Keep Security Controls and Compliance Policies Updated
Just like you regularly update your phone to keep it running smoothly, your digital signature tools need regular updates too. Here’s why:
Track New and Emerging Threats
For one, hackers are always changing up their tactics and finding new ways to slip past security defenses. So if you don’t install the latest updates that patch potential weak spots? You’re leaving yourself wide open to attacks like ransomware, identity theft and phishing.
Another smart move is to understand how your connection is protected and what tools actually safeguard your data. Knowing the difference between proxy and VPN can help you choose the right level of privacy and security for your online activities.
Update Hardware, Not Only Software
It’s not just the software you need to update either. If you use any physical devices for signing, like an HSM or TPM, they need to stay updated too. Treat them the way you would treat any other piece of security hardware, and check firmware and storage on a schedule so your signing devices keep working without interruptions.
Evolving Compliance Standards
Another reason to update regularly: rules and regulations for digital signatures evolve over time. So even if your tools were fully compliant in the past, they can get outdated real quick. Staying current keeps you legit in the eyes of the law.
Show Signers Their Data Is Protected
Updating reinforces trust and confidence with your clients! It shows them you take security super seriously around here. And that peace of mind can go a long way in their decision to stick with your biz and share sensitive info.
Keep Signing Workflows Fast
Regular updates often come with performance enhancements. They’re not just about security; they also ensure that your digital signature tools are running at peak efficiency.
It’s easy to hit ‘remind me later’ on updates, but in the world of digital security, procrastination can be costly. So while updating stuff is about as exciting as watching paint dry (blah!), just remember – it’ll save you major headaches down the road!
4. Verify the Signer’s Identity Before Signing
The goal here is to make absolutely sure that the person signing the document is who they claim to be. It’s like checking the ID at the door, but more high-tech.
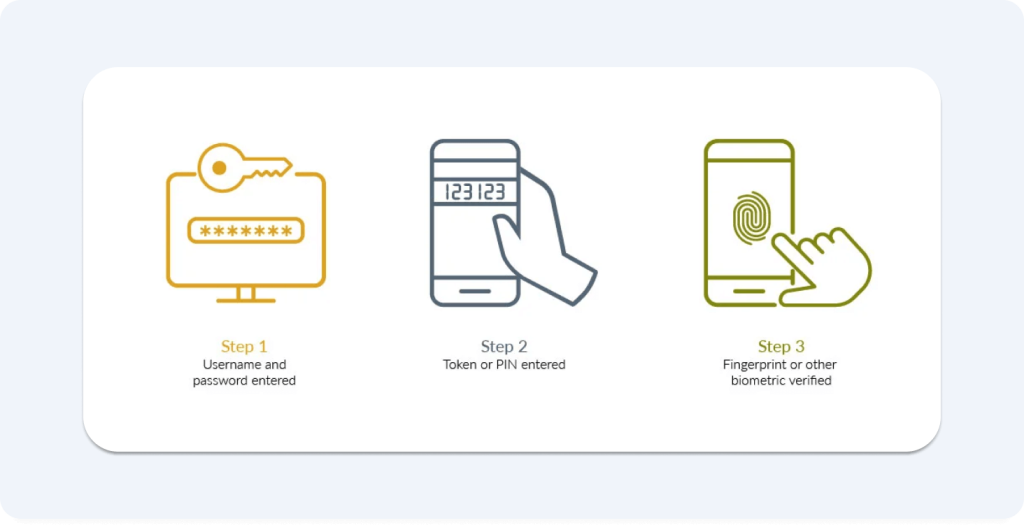
Multi-Factor Authentication (MFA)
You need more than just a password (something you know). You might also need a phone or a fingerprint (something you have or something you are). This makes it much harder for an imposter to sneak in.
source: RSA
Biometric Verification
Biometrics can include fingerprint scanning, facial recognition, or even voice analysis.
Document Analysis Tools
Some systems can analyze the document and its signing process for any unusual patterns or anomalies, adding an extra layer of scrutiny.
5. Use Timestamps and Audit Trails for Proof
Time-stamping is like putting a date stamp on a letter but in a way that can’t be tampered with. It’s crucial for maintaining the integrity of the document over time.
Secure Time-Stamping Service
These services record the exact time a document was signed and seal it with their stamp. It’s like having a trusted referee who says, “Yes, this happened at this time.”
Audit Trail
This includes a detailed log of all actions related to the document, including when it was accessed, viewed, and signed.
Legal And Historical Proof
Imagine if someone tried to claim that a document was signed last year when it was actually signed yesterday. Time-stamping prevents such scenarios as it makes it clear when the event actually happened.
This ensures that every action on the document is historically accurate and legally defensible.
Consistency Across Time Zones
It’s a global world. Documents cross borders and time zones, so having a standardized time reference is a great idea. Time-stamping services usually use Coordinated Universal Time (UTC), ensuring that the timestamp is consistent, regardless of the parties’ location.
6. Use Advanced or Qualified Signatures for High-Risk Documents
Think of this as getting an official wax seal from a king or queen. A Certificate Authority (CA) is like this royal figure in the digital world. They prove the signer’s identity and the authenticity of their signature.
Check For Compliance With Legal Requirements
When we talk about digital signatures, it’s not a one-size-fits-all scenario. The legal landscape is pretty diverse. Here’s what’s interesting:
Regional Variations
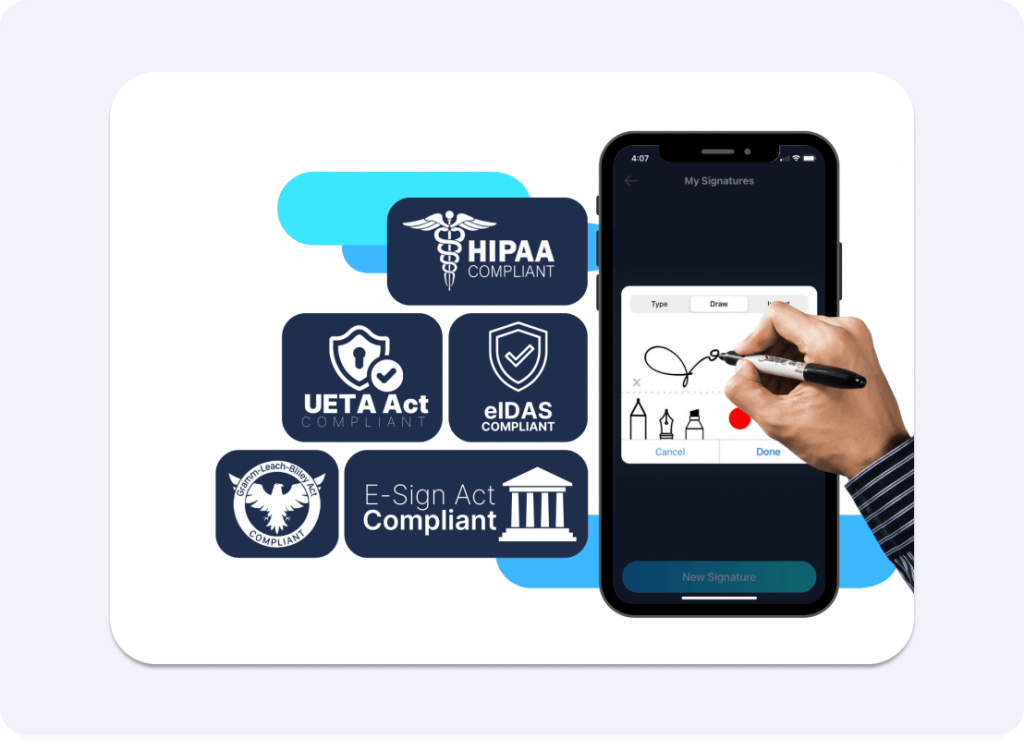
In the U.S., the ESIGN Act and UETA provide the legal framework, while in Europe, it’s the eIDAS. Each region, sometimes each country, has its own rules.
For instance, in some places, a simple electronic signature is enough for most documents, but in others, you might need a more advanced or qualified electronic signature, especially for legal or governmental documents.
source: Fill
Industry-Specific Regulations
If you’re in healthcare, finance, or government sectors, there might be additional layers of compliance. HIPAA is non-negotiable in healthcare, so any system that stores or transmits signed patient documents has to meet its requirements as well.
On the other hand, Electronic Signatures in Global and National Commerce Act (E-SIGN) provides the legal framework for electronic signatures in the federal government.
They ensure that e-signatures are as legally binding as their handwritten counterparts, provided they meet certain criteria.
Follow Changes in Signature Regulations
Laws aren’t static, right? They evolve. So, keeping up-to-date with the latest legal changes is crucial. It’s a bit like chasing a moving target, but it’s essential.
7. Train Users to Avoid Common E-Signature Mistakes
Now, this is where human factors come into play. Technology is one part of the puzzle, but people are another significant part. Here’s the deal:
Make Signers Aware of the Risks
Most users might not know the gravity of an electronic signature. It’s like a handwritten signature but in the digital world. So, treating it with the same level of seriousness is important. Whether you’re signing a client contract or approving an internal policy, understanding what you commit to electronically is crucial.
Never Share Signing Credentials
The private key is like the key to your house. You wouldn’t just hand it out to anyone, right? Users need to understand that sharing their private key is a big no-no.
Implications Of Signing
Sometimes people might just click ‘sign’ without thinking. They need to understand that a digital signature holds legal weight. It’s like saying, “Yes, I agree, and you can hold me to this.”
8. Review Signed Documents, Access and Retention Policies Regularly
Think of this as a health check for your digital signature processes. It’s not just a one-time setup and forget scenario. Here’s why it’s crucial:
Review Against New Threat Patterns
Cyber threat patterns are like viruses; they evolve constantly. So, continually reviewing your security measures is like getting your regular health check-ups to stay ahead of new and emerging attacks.
Policy And Procedure Review
It’s not just about the tech. Look at how the whole process is managed. Are the policies still relevant? Are the procedures foolproof?
Tech Updates
Are you using the latest version of your digital signature software? Is your hardware still up to par? Keeping tech updated is as essential as updating your phone or computer.
Final Thoughts on Electronic Signature Best Practices
There you have it. The thing worth remembering is that no single control makes an electronic signature safe, and secure software on its own is the piece people most often mistake for a finished job. What holds up under challenge is the combination: a compliant platform, signer verification matched to the risk, recorded consent and intent, a complete audit trail, document integrity you can demonstrate, and retention that keeps all of it together.
Start with the documents that would hurt most if they were disputed, and get those right first. The rest of your signing workflows can follow the same pattern once you know what good looks like. It is a lot cheaper to build the habit now than to reconstruct the evidence later.
Which Documents May Still Require Wet-Ink Signatures?
Electronic signature laws come with carve-outs. They are narrower than most people expect, but they are real, and depending on the jurisdiction some documents sit outside ESIGN, UETA or eIDAS altogether. So an electronic signature you collect on those may simply not count, however careful your process was.
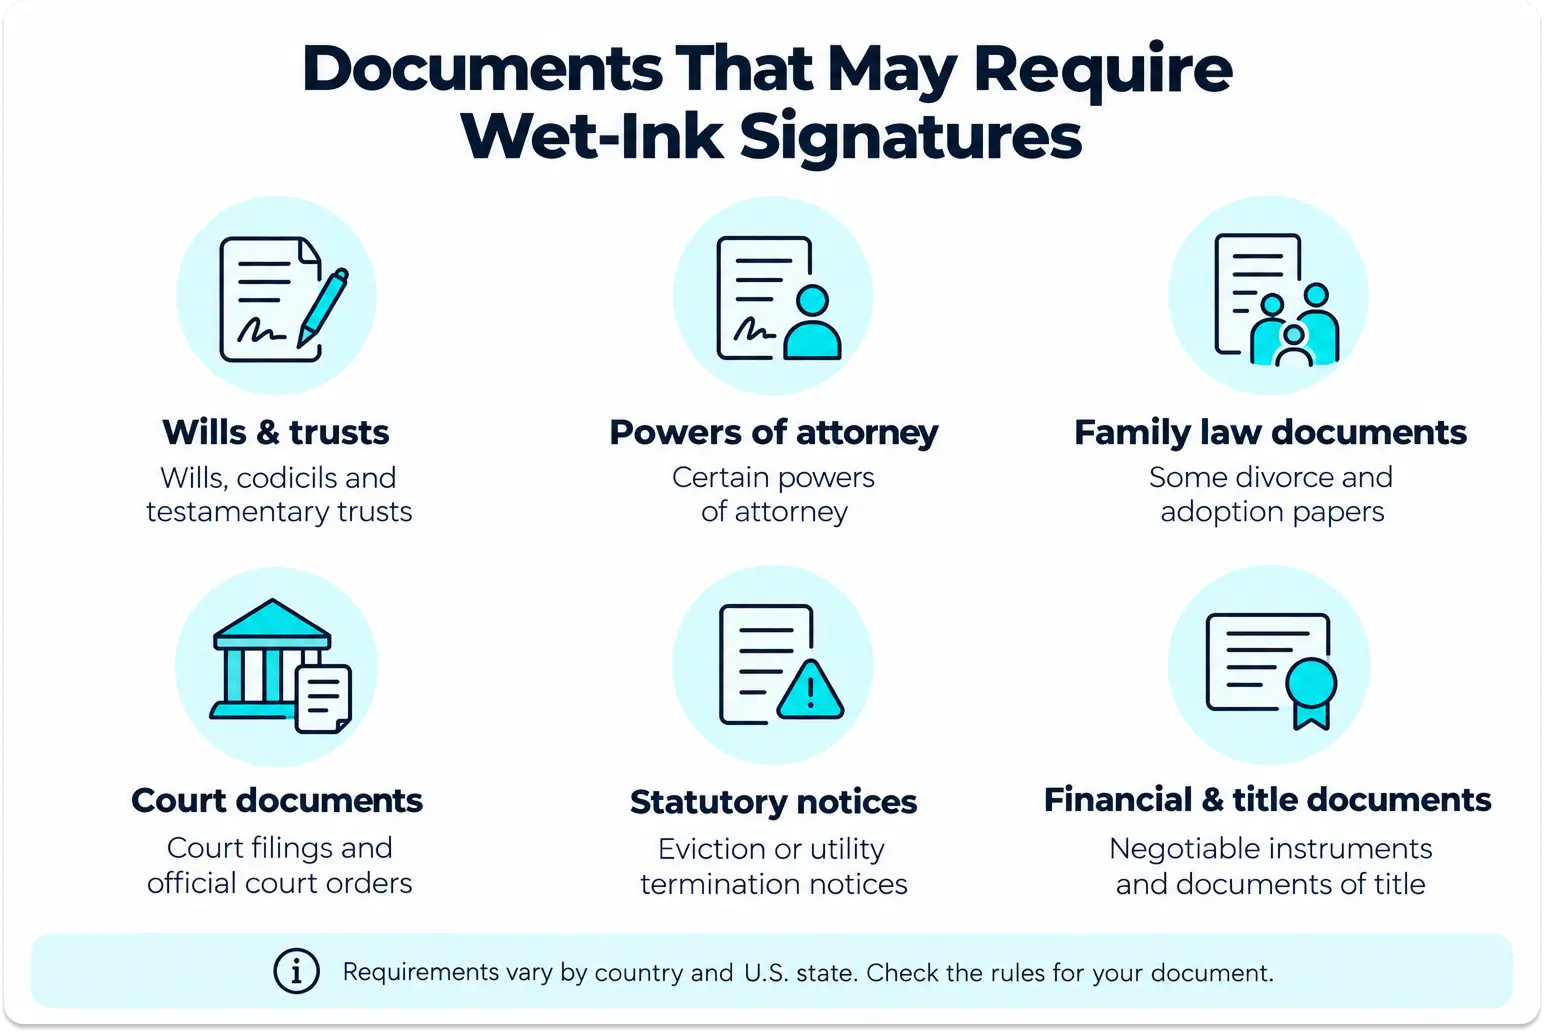
The list shifts from country to country and, in the US, from state to state, so treat it as a prompt to check rather than as an answer. If a document type you handle sits anywhere near this list, confirm the local rule before you send it out for electronic signing.
Cross-Border Electronic Signatures: What to Check Before Signing
A signature that is perfectly valid where you sit can be worth much less where your counterparty sits, so international agreements deserve a few checks before anyone clicks anything.
- Which law governs the agreement, and does it recognise electronic signing?
- Where is each signer physically located at the moment they sign?
- Is this document type excluded from electronic signing in either country?
- What signature level does the stricter side expect: simple, advanced or qualified?
- Which identity verification methods are accepted there, and does your platform support them?
- Where will the signed copy and the audit trail be stored, and does that satisfy local data rules?
- Is the value or the risk high enough to justify local counsel before signing?
None of these takes long to answer once, and the answers usually hold for a whole class of agreements. The expensive version is finding the mismatch after a deal has already gone wrong.
Electronic Signature Implementation Checklist for Businesses
If you are rolling an e-signature solution out across a business rather than signing the occasional contract, work through these in order:
- Identify which document types you actually sign electronically.
- Classify each type by risk and legal exposure.
- Choose the signature level each risk class requires.
- Verify the legal requirements in every jurisdiction you sign in.
- Configure signer authentication to match each risk class.
- Turn on audit trails and confirm what they capture.
- Define retention periods and storage for signed documents.
- Train the people who send and sign documents.
- Audit the whole process on a fixed schedule.
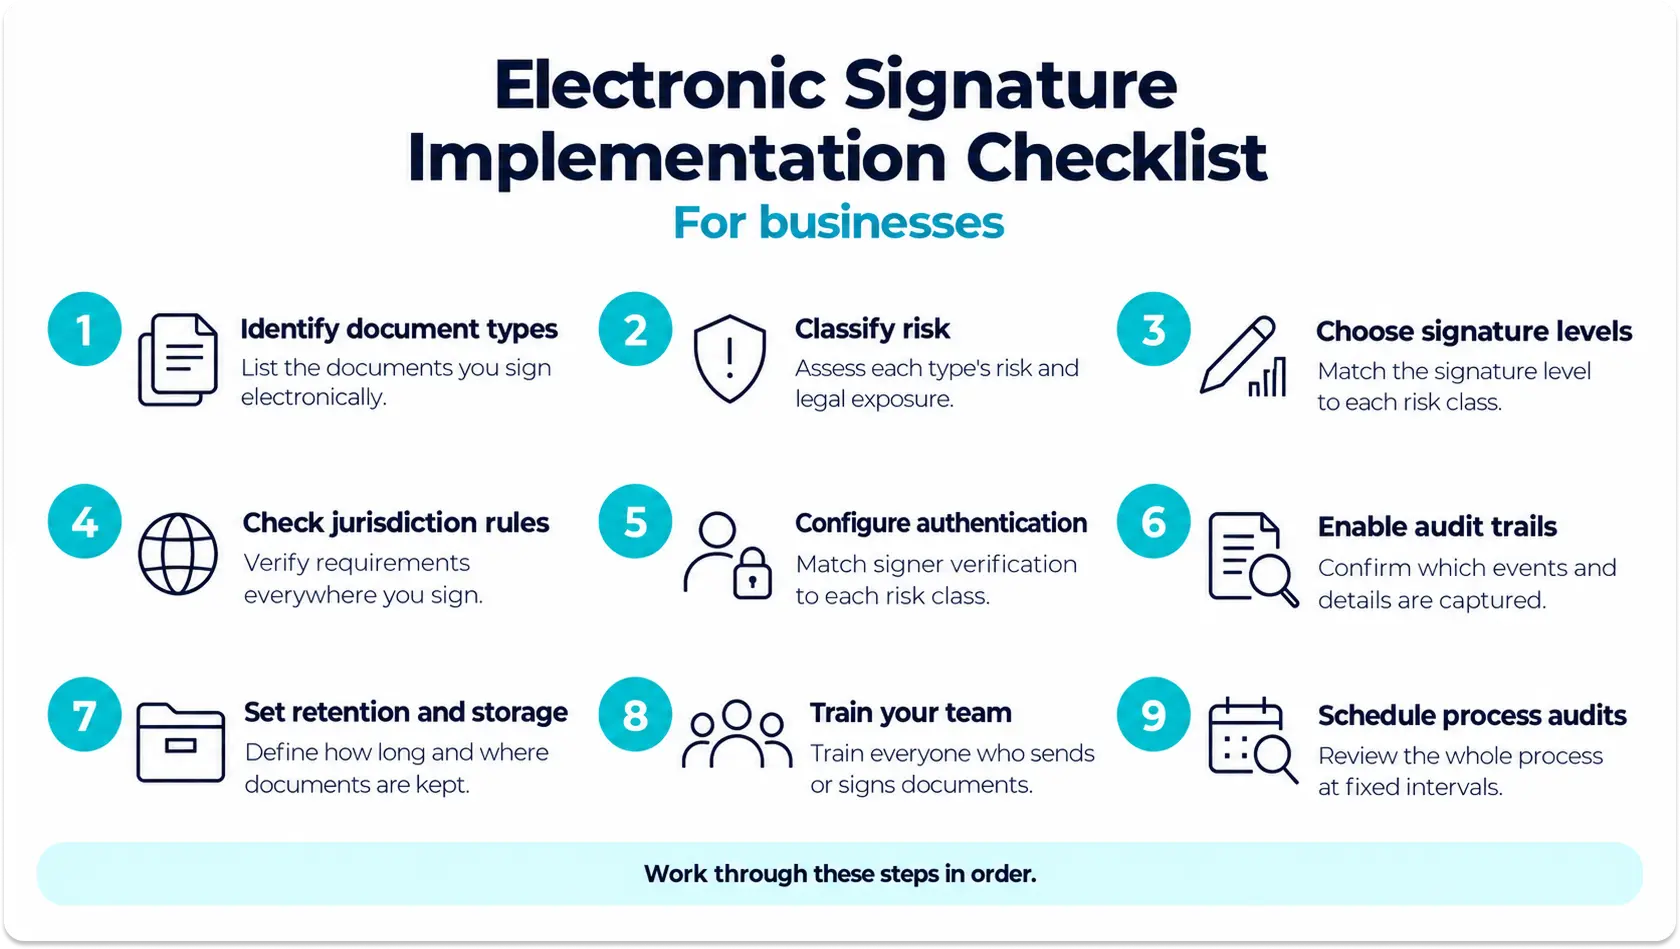
Steps five through nine are the best practices above, in short form, so use them as a reminder rather than a second lesson.
Common Electronic Signature Risks and How to Prevent Them
Most electronic signature failures are not exotic attacks. They are ordinary process gaps, and they only become visible when someone challenges the document.
| Risk | What it looks like | How to prevent it |
|---|---|---|
| Weak authentication | Anyone holding the link can sign | Match authentication to document risk, require MFA above low risk |
| Shared signing links | A link forwarded to a colleague who signs instead | Send a unique link per signer and expire it after use |
| Forged or unverified identity | The signer is not who the email suggests | Add ID document or knowledge-based checks on high-risk documents |
| Missing consent record | No proof the signer agreed to sign electronically | Capture the consent event and keep it in the audit trail |
| Document tampering | The file is edited after signing | Use certificate-based signatures, so any change breaks the seal |
| Expired certificates | The signature shows as invalid on verification | Track certificate expiry dates and renew before they lapse |
| Non-compliant vendor | The platform lacks ESIGN, UETA or eIDAS support | Confirm compliance and security standards before you buy |
| Lost audit trail | The signed copy survives, the evidence around it does not | Store the audit trail with the document under one retention policy |
Work down the right-hand column and you have most of a security and compliance policy written already, plus a checklist for judging any electronic signature solution you are considering.
Common Use Cases for Electronic Signatures
The documents you sign electronically cluster by department more than by industry. Your sales and procurement teams run contracts, quotes, purchase orders and supplier agreements through it, and HR is usually close behind with offer letters, employment contracts, policy acknowledgements and NDAs. Your finance and legal teams add invoices, loan documents, board consents and settlement agreements. Regulated sectors go further still, because healthcare, real estate and insurance each carry their own consent forms, disclosures and closing packets. What these share is not the content but the workflow: a document that needs a named person’s agreement, on a deadline, from wherever that person happens to be. That is where the benefits of electronic signatures show up most clearly, because the business processes you streamline are the ones that used to wait on someone being in the office.
FAQ: Electronic Signature Best Practices
Are electronic signatures legally binding?
In most countries, yes. Laws such as the ESIGN Act, UETA and eIDAS give your electronic signature the same legal status as a handwritten one, as long as consent, intent, signer identification and document integrity can be shown. A short list of document types stays excluded.
What makes an electronic signature secure?
Security comes from the evidence around the signature rather than from the mark itself. Reliable signer authentication, encryption in transit and at rest, a complete audit trail and tamper detection on the signed file are the security features that make your signature hard to dispute later.
What is the difference between an electronic signature and a digital signature?
An electronic signature is any electronic indication of intent to sign. A digital signature is one specific kind of it, built on public key infrastructure and a digital certificate, so any change to the file you signed becomes detectable.
Do electronic signatures need an audit trail?
The law rarely demands one in those words, but in practice your audit trail is what proves the signature. Without a record of who signed, when, from where and after what consent, you are left asserting things you cannot evidence.
When do I need a qualified electronic signature?
Mostly in the EU, and mostly for regulated or registry-facing paperwork: property transfers, corporate filings, some public sector forms and certain cross-border agreements. Outside those cases a standard or advanced electronic signature is usually enough for what you are signing.
What documents still require wet-ink signatures?
Depending on the jurisdiction, wills, certain powers of attorney, some family law documents, court filings, statutory notices and negotiable instruments. The exclusions vary by country and, in the US, by state, so confirm locally before you sign.
How should businesses store electronically signed documents?
Keep the signed file and its audit trail together, under a retention policy that says how long you hold each document type and who may access it. Where you store them matters too, because data protection rules follow the personal data inside.